Skip to content

$ whoamiOffensive Security, Researcher, Bug Hunter

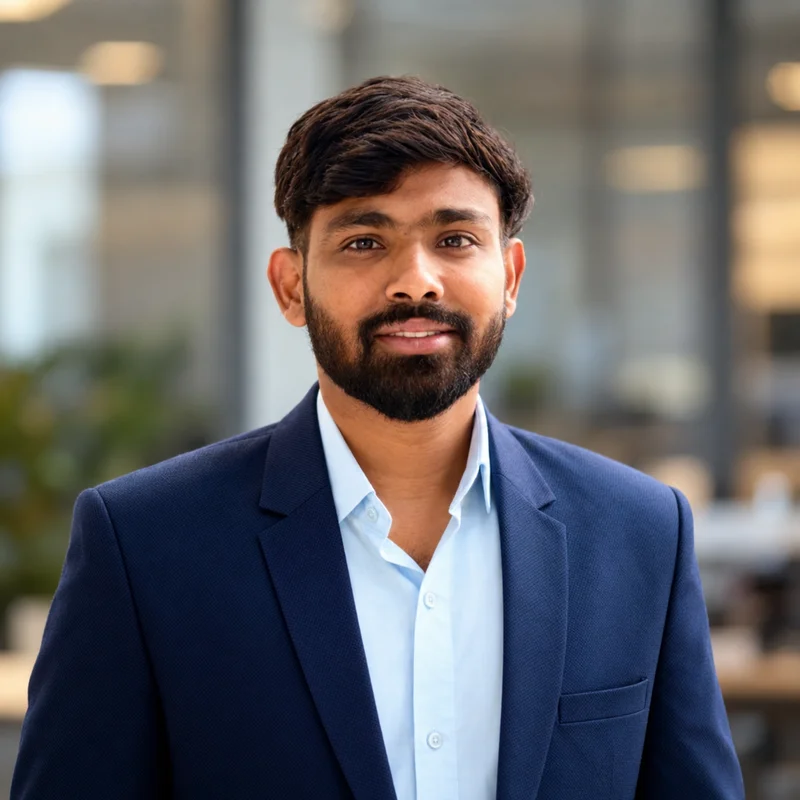
Hi👋,I'm

I explore the flaws behind how things are built, and research what it takes to secure the environment around them.

  • Cyber Security Engineer@ QOS Technology Private Limited
  • Delhi, India
Raju Ranjan
CEH v12 certified

01 // about

Breaking things to understand how to protect them

I look at systems the way an attacker would, so teams can see how they break before someone else does.

Now:Cyber Security Engineer @ QOS Technology Private Limited· since Jun 2025

01

An attacker's-eye view

Web and Android applications, Wi-Fi networks and internal infrastructure, tested the way a real adversary would approach them: from recon to proof of impact.

02

Research defenders can use

I study the building blocks defenders rely on and turn what I find into practical guidance. Author of the published paper "Web Vulnerabilities Modulation".

03

Proven under pressure

CEH v12 certified, Grand Finalist at the KAVACH national cybersecurity hackathon, and a Gold Medal for academic excellence.

Years in cybersecurity
+
National hackathon finals & podiums
Published research paper
Gold medal for academic excellence
The longer version

I studied Computer Science with a specialisation in Information Security at Chandigarh University, where I spent more weekends at hackathons than anywhere else, and earned a gold medal for the most participations.

I joined QOS Technology as a Cyber Security Intern in April 2025, and two months later stepped up to Cyber Security Analyst, where I run offensive assessments and security research.

02 // skills

Attack surface I work across

Offensive security across the full stack, from the browser and the phone to the airwaves and the server room.

Red Teaming

Adversary emulation that tests people, process and technology together, from initial access to objective.

  • Adversary emulation
  • Initial access
  • Lateral movement
  • Social engineering

Web Application Testing

Finding and proving vulnerabilities in web apps and APIs, beyond what scanners catch.

  • OWASP Top 10
  • Auth & session flaws
  • Business logic
  • API security

Android Application Testing

Static and dynamic analysis of Android apps and the backends they talk to.

  • Static analysis
  • Dynamic instrumentation
  • Insecure storage
  • SSL pinning bypass

Wi-Fi Pentesting

Assessing wireless networks for weak configurations, rogue access and credential exposure.

  • WPA/WPA2 attacks
  • Rogue access points
  • Handshake capture
  • Wireless recon

Infrastructure Pentesting

Internal and external network assessments, from reconnaissance to privilege escalation.

  • Network recon
  • Service exploitation
  • Privilege escalation
  • Active Directory

03 // journey

From the classroom to the red team

Education, competitions, research and work, in the order they happened.

  • Education
  • Certification
  • Achievement
  • Research
  • Work
  1. · Education

    B.E. Computer Science & Engineering

    Chandigarh University

    Specialisation in Information Security. Received the Academic Excellence Award (Gold Medal) for the most hackathon participations.

  2. · Certification

    Certified Ethical Hacker (CEH v12)

    EC-Council

    Certified in the methodology and tooling of ethical hacking.

  3. · Achievement

    National hackathon circuit

    KAVACH · Intel oneAPI × IIT Roorkee · Smart India Hackathon

    Grand Finalist (top 3) at KAVACH, 5th place at Intel oneAPI × IIT Roorkee, and 2nd Runner-Up at the Smart India Hackathon qualifiers.

  4. · Research

    Published research

    ResearchGate

    Authored "Web Vulnerabilities Modulation".

  5. · Work

    Cyber Security Intern

    QOS Technology Private Limited

    Two-month internship in offensive security assessments and security research.

  6. · WorkNow

    Cyber Security Engineer

    QOS Technology Private Limited

    Offensive security assessments and security research.

  7. Next

    What's next

04 // projects

Projects & write-ups

Tools, research and write-ups I've built along the way.

Shipped

AirSniffer

A single Bash console for a whole Wi-Fi engagement - discover and audit WEP, WPA/WPA2, WPA3-SAE and WPS, run the deauth → handshake capture → offline crack chain, and stand up a vendor-matched evil twin. Authorized testing only.

  • #wi-fi-security
  • #bash
  • #red-team
Coming soon

Project Two

A short, one or two line summary of what this project does and why it matters.

  • #android
  • #research
Coming soon

Project Three

A short, one or two line summary of what this project does and why it matters.

  • #tooling
  • #automation

05 // achievements

Certifications, hackathons & recognition

  • Awards

    Academic Excellence Award

    Chandigarh University

    Gold Medal, most hackathon participations

  • 2024

    Research

    Published Researcher

    ResearchGate · Web Vulnerabilities Modulation

    Author

  • 2023

    Hackathons

    Grand Finalist

    KAVACH National Cybersecurity Hackathon

    Top 3 Teams

  • 2023

    Hackathons

    5th Place

    Intel oneAPI Hackathon × IIT Roorkee

    Top 5

  • 2023

    Hackathons

    2nd Runner-Up

    Smart India Hackathon Qualifiers

    Top 3

  • 2023

    Certifications

    CEH v12 Certified

    EC-Council

    Certified Ethical Hacker

06 // now

What I'm doing right now

last updated:

~/now - status
  • Cyber Security Analyst at QOS Technology

    Running offensive security assessments and researching new attack surface.

  • Bug hunting

    Hunting for vulnerabilities in web applications and APIs.

  • Writing

    Turning research and findings into write-ups on this blog and on Medium.

07 // focus

Current focus & interests

  • Red Teaming

    Realistic adversary emulation end-to-end.

  • Web & API Security

    Logic flaws and auth bugs that scanners miss.

  • Mobile Security

    Android app internals and runtime analysis.

  • Security Research

    Studying how vulnerabilities emerge from the way systems are built.

08 // roadmap

What's next

The goals I'm working towards.

  1. 01

    Advanced offensive certification

    [ ] Planned

    Level up with a hands-on offensive security certification.

  2. 02

    More published research

    [ ] Planned

    Publish follow-up research on web vulnerability patterns.

  3. 03

    Open-source tooling

    [ ] Planned

    Release tools that automate parts of my testing workflow.

  4. 04

    Hall of fame entries

    [~] In progress

    Grow a track record of responsible disclosures.

09 // blog

Latest from the blog

cd ~/blog

10 // contact

Reach me

Let's talk security

Whether it's a pentest, a research collaboration, a bug bounty find or just a conversation about offensive security, my inbox is open.